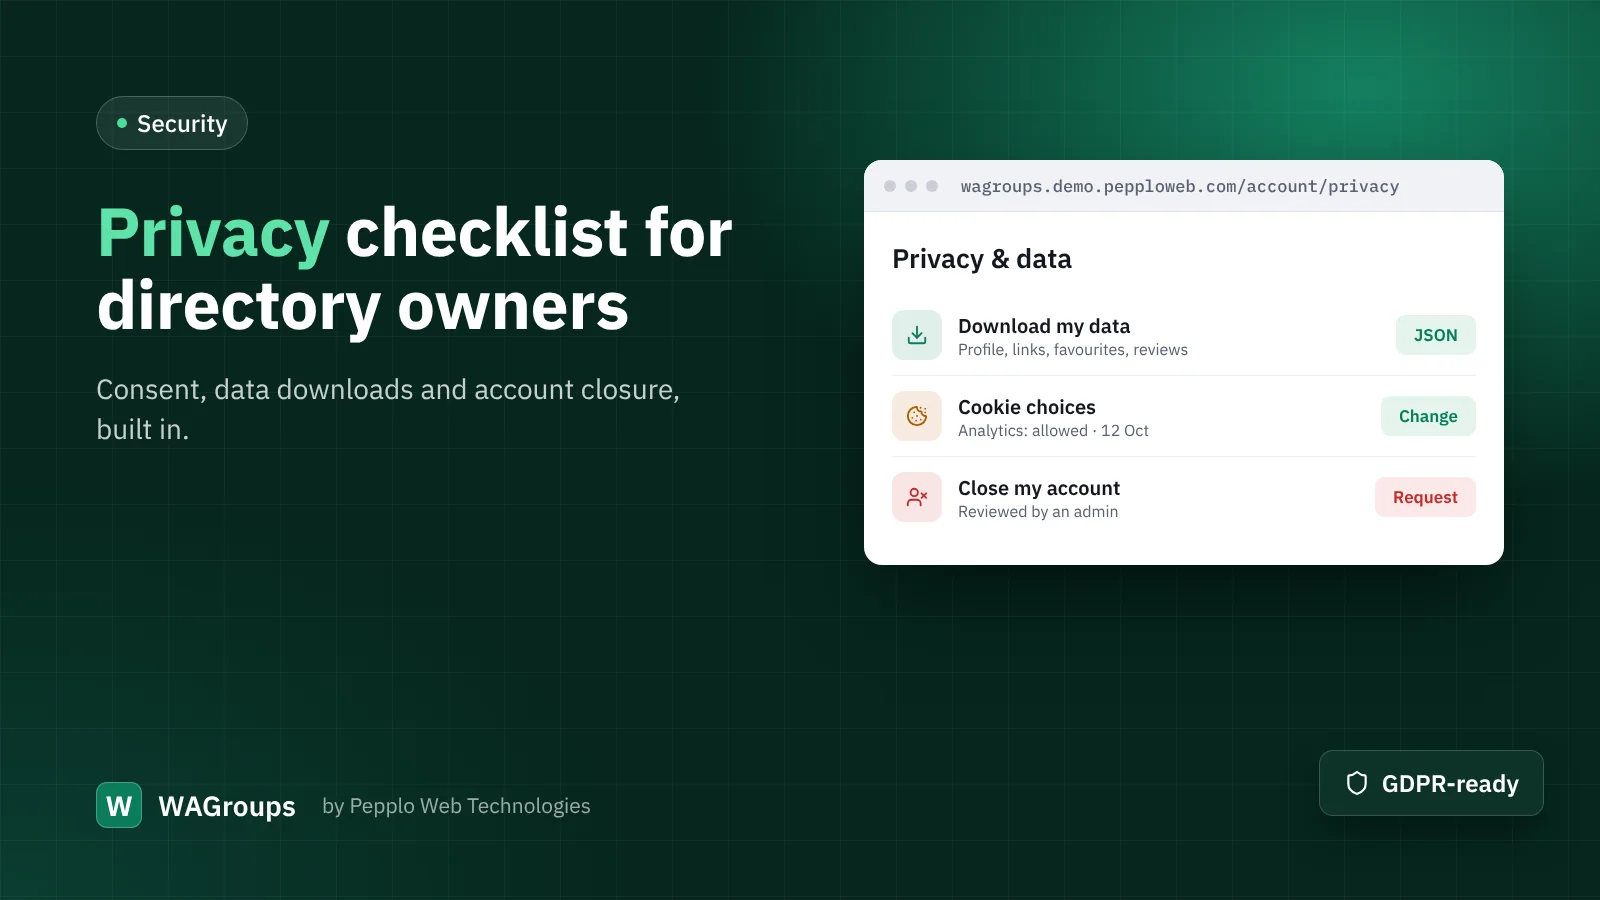
A group directory collects less personal data than most websites — but it still collects some: member accounts, IP addresses, analytics and, if you use them, identity documents. Privacy laws such as the GDPR in Europe and the DPDP Act in India expect you to handle that data openly. WAGroups gives you the tools; this checklist helps you use them. (This is practical guidance, not legal advice.)
1. Say what you collect
WAGroups includes a privacy policy template. Review it, fill in your company details and mention anything you added, such as an analytics tool or an advertising network.
2. Ask before tracking
Switch on Privacy and GDPR › Cookie consent. Analytics only load after a visitor agrees, and every choice is recorded in the consent log with date and time — useful if you are ever asked to prove consent.
3. Let people download their data
Members can download everything about them from Privacy & data in their account: profile, links, favourites, reviews and more, as a JSON file. Nothing to do on your side.
4. Let people leave
Choose whether accounts close immediately or after an admin reviews the request. When an account closes, favourites, reviews and API keys are deleted, and public links stay listed without the member's name, email or IP address.
5. Keep only what you need
- Turn on "anonymise IPs" in Visitors History if you do not need full addresses.
- Set a retention for backups so old copies are deleted automatically.
- Only use KYC if you really need identity documents, and delete submissions you no longer need.
6. Protect the panel
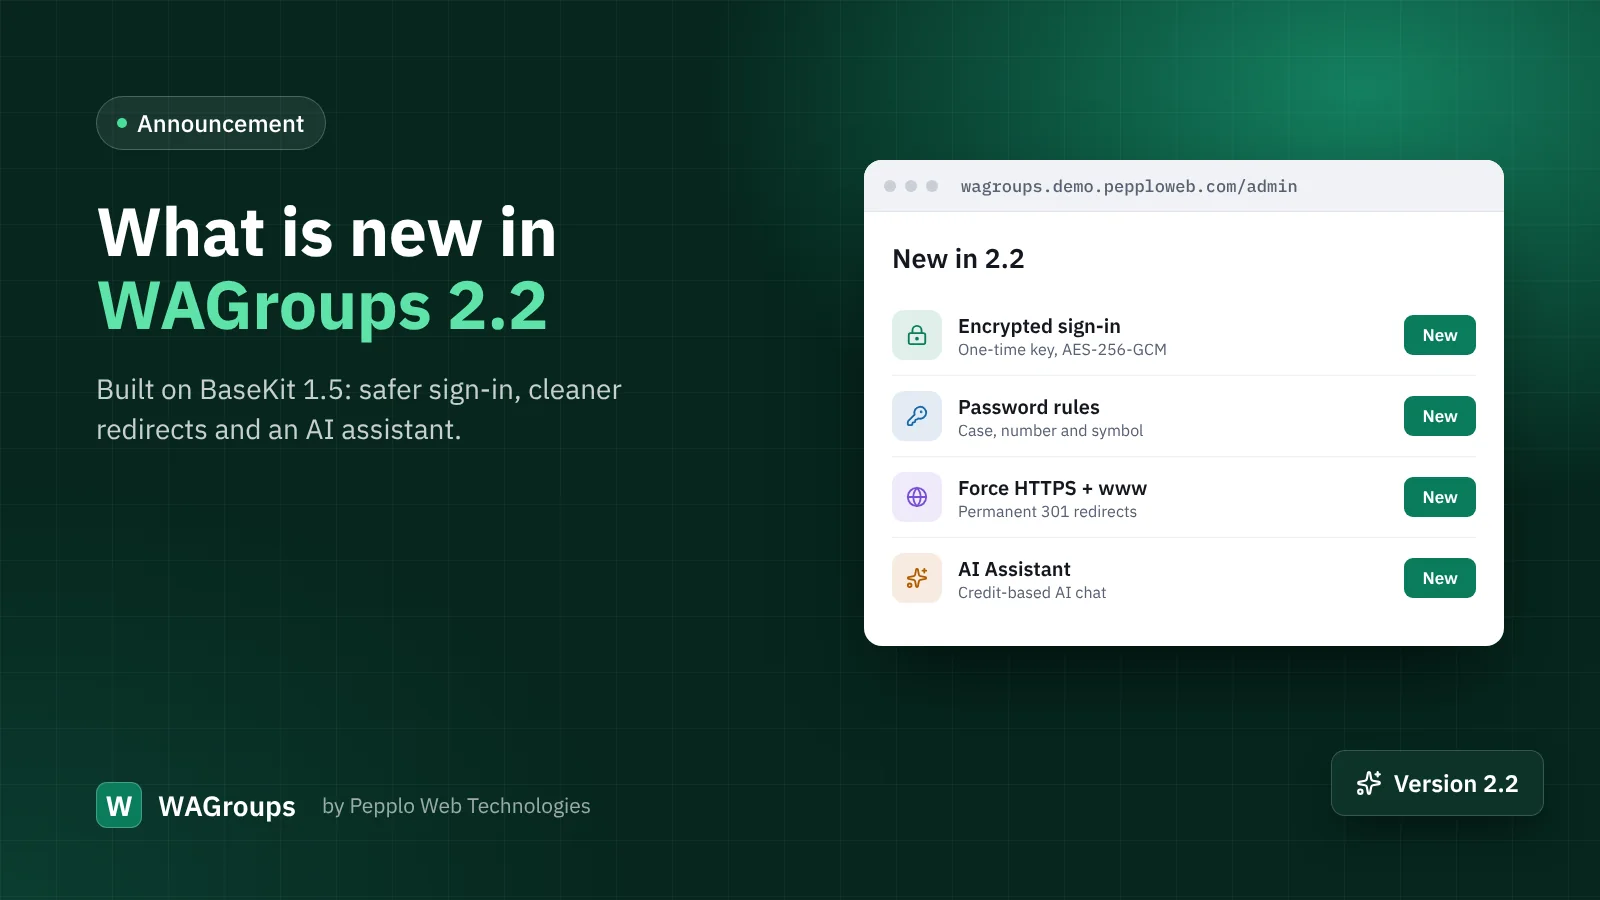
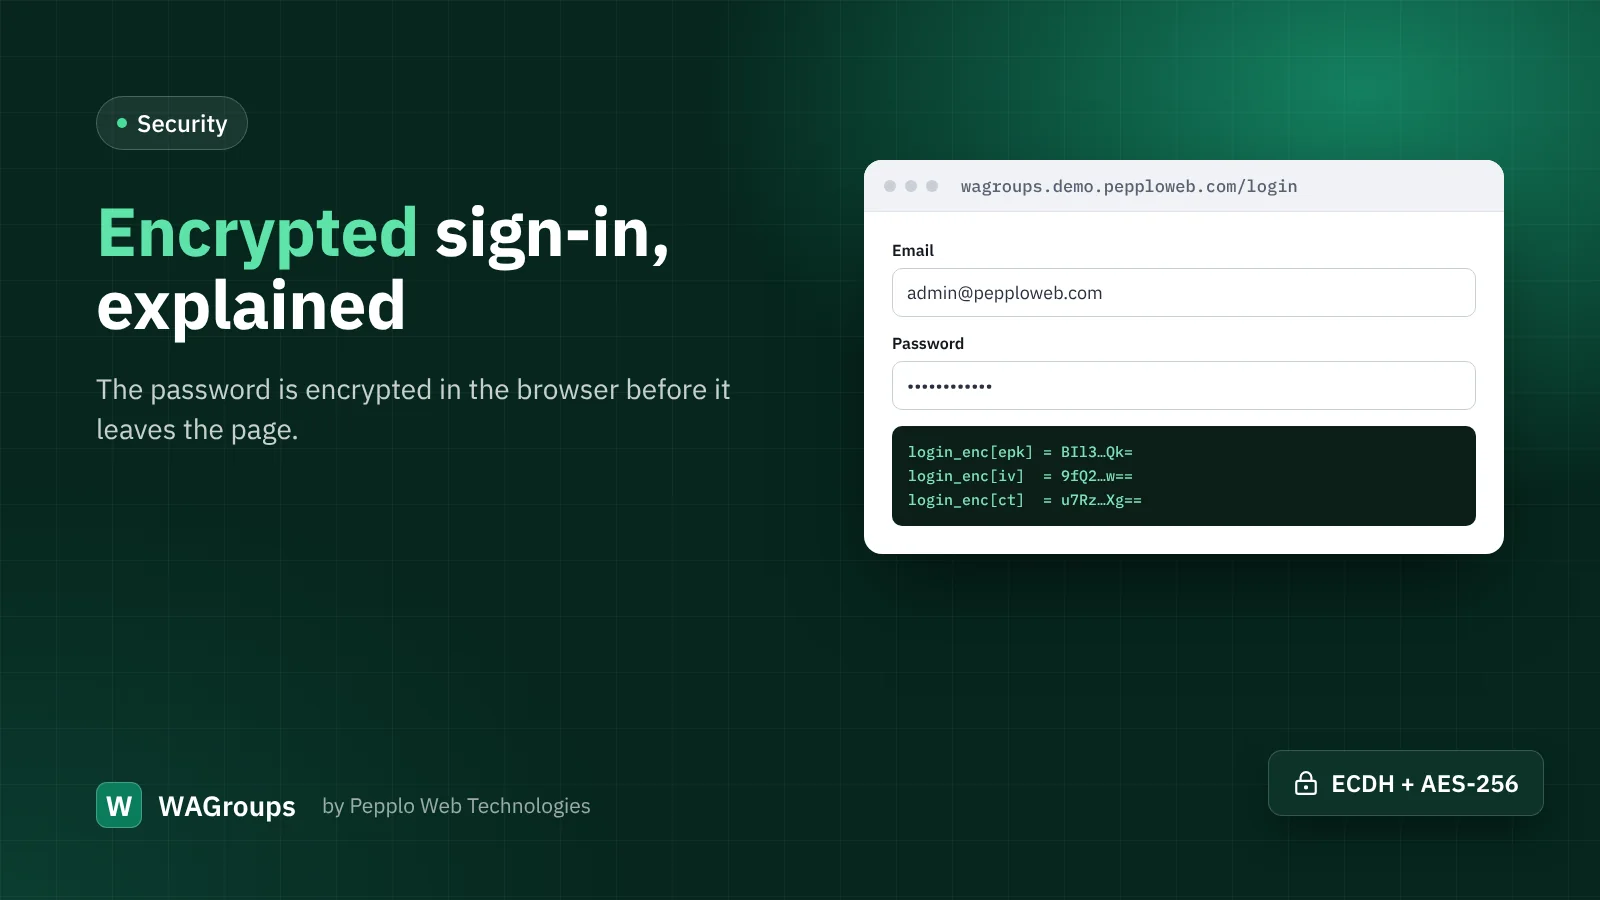
Two-step verification for staff, encrypted sign-in and strong password rules protect the place where all of this data lives.
0 comments